Cogito Group and SecureSME
Challenge
Outages and data loss often start with expired, weak or compromised credentials. When a certificate expires without renewal, the service that relies on it stops: users cannot log in, applications cannot connect and transactions fail. An attacker can break or steal a weak key or certificate. This compromise allows an attacker to impersonate a trusted user or service and read or take protected data. Data can be lost even when it is never stolen, because whoever holds the keys decides who now owns it.
Solution
Cogito Group’s Jellyfish removes each cause. It finds every certificate and key in use and renews them automatically before they expire. It issues credentials using only approved algorithms and at set key strengths, flags weak ones for replacement and keeps private keys in hardware. If a credential is compromised, Jellyfish can revoke it straight away. It then tell other systems that rely on it to stop trusting it. With bring-your-own-key options, even in the cloud, the customer, not a cloud provider or third party, holds the keys and keeps control of its data. Jellyfish is delivered as a service, with on-premises deployment an option for larger organisations.
Who We Are
One platform covers certificates, keys, identity and security operations, so whatever a customer buys first, the next service plugs into the same portal.
Cogito Group is an award-winning company specialising in authentication, cloud security, identity management and data protection. It serves government, finance, utilities and telecommunications companies in multiple countries, counting around 10,000, organisations as customers. Cogito has been in operation since 2011. Cogito Group protects the methods people use to access information, and protects data from unauthorised access, disclosure and alteration, whether by an outside party or a trusted insider with malicious intent. This helps detect and prevent fraud.
SecureSME is the Cogito Group as-a-service brand for small to medium businesses, managed service providers and resellers. It delivers PKI, certificate lifecycle management and key management with self-service sign-up and published pricing.
Jellyfish, Delivered as a Service
Every service runs on Jellyfish, Cogito Group’s modular platform for digital trust. It unifies identity, device, credential and certificate management under one control plane. Each module can be adopted on its own and expanded over time, so security capability grows with the organisation while operational effort and cost fall.
Jellyfish is delivered as a service, managed by Cogito Group. Larger organisations that need full control can also deploy it on premises.
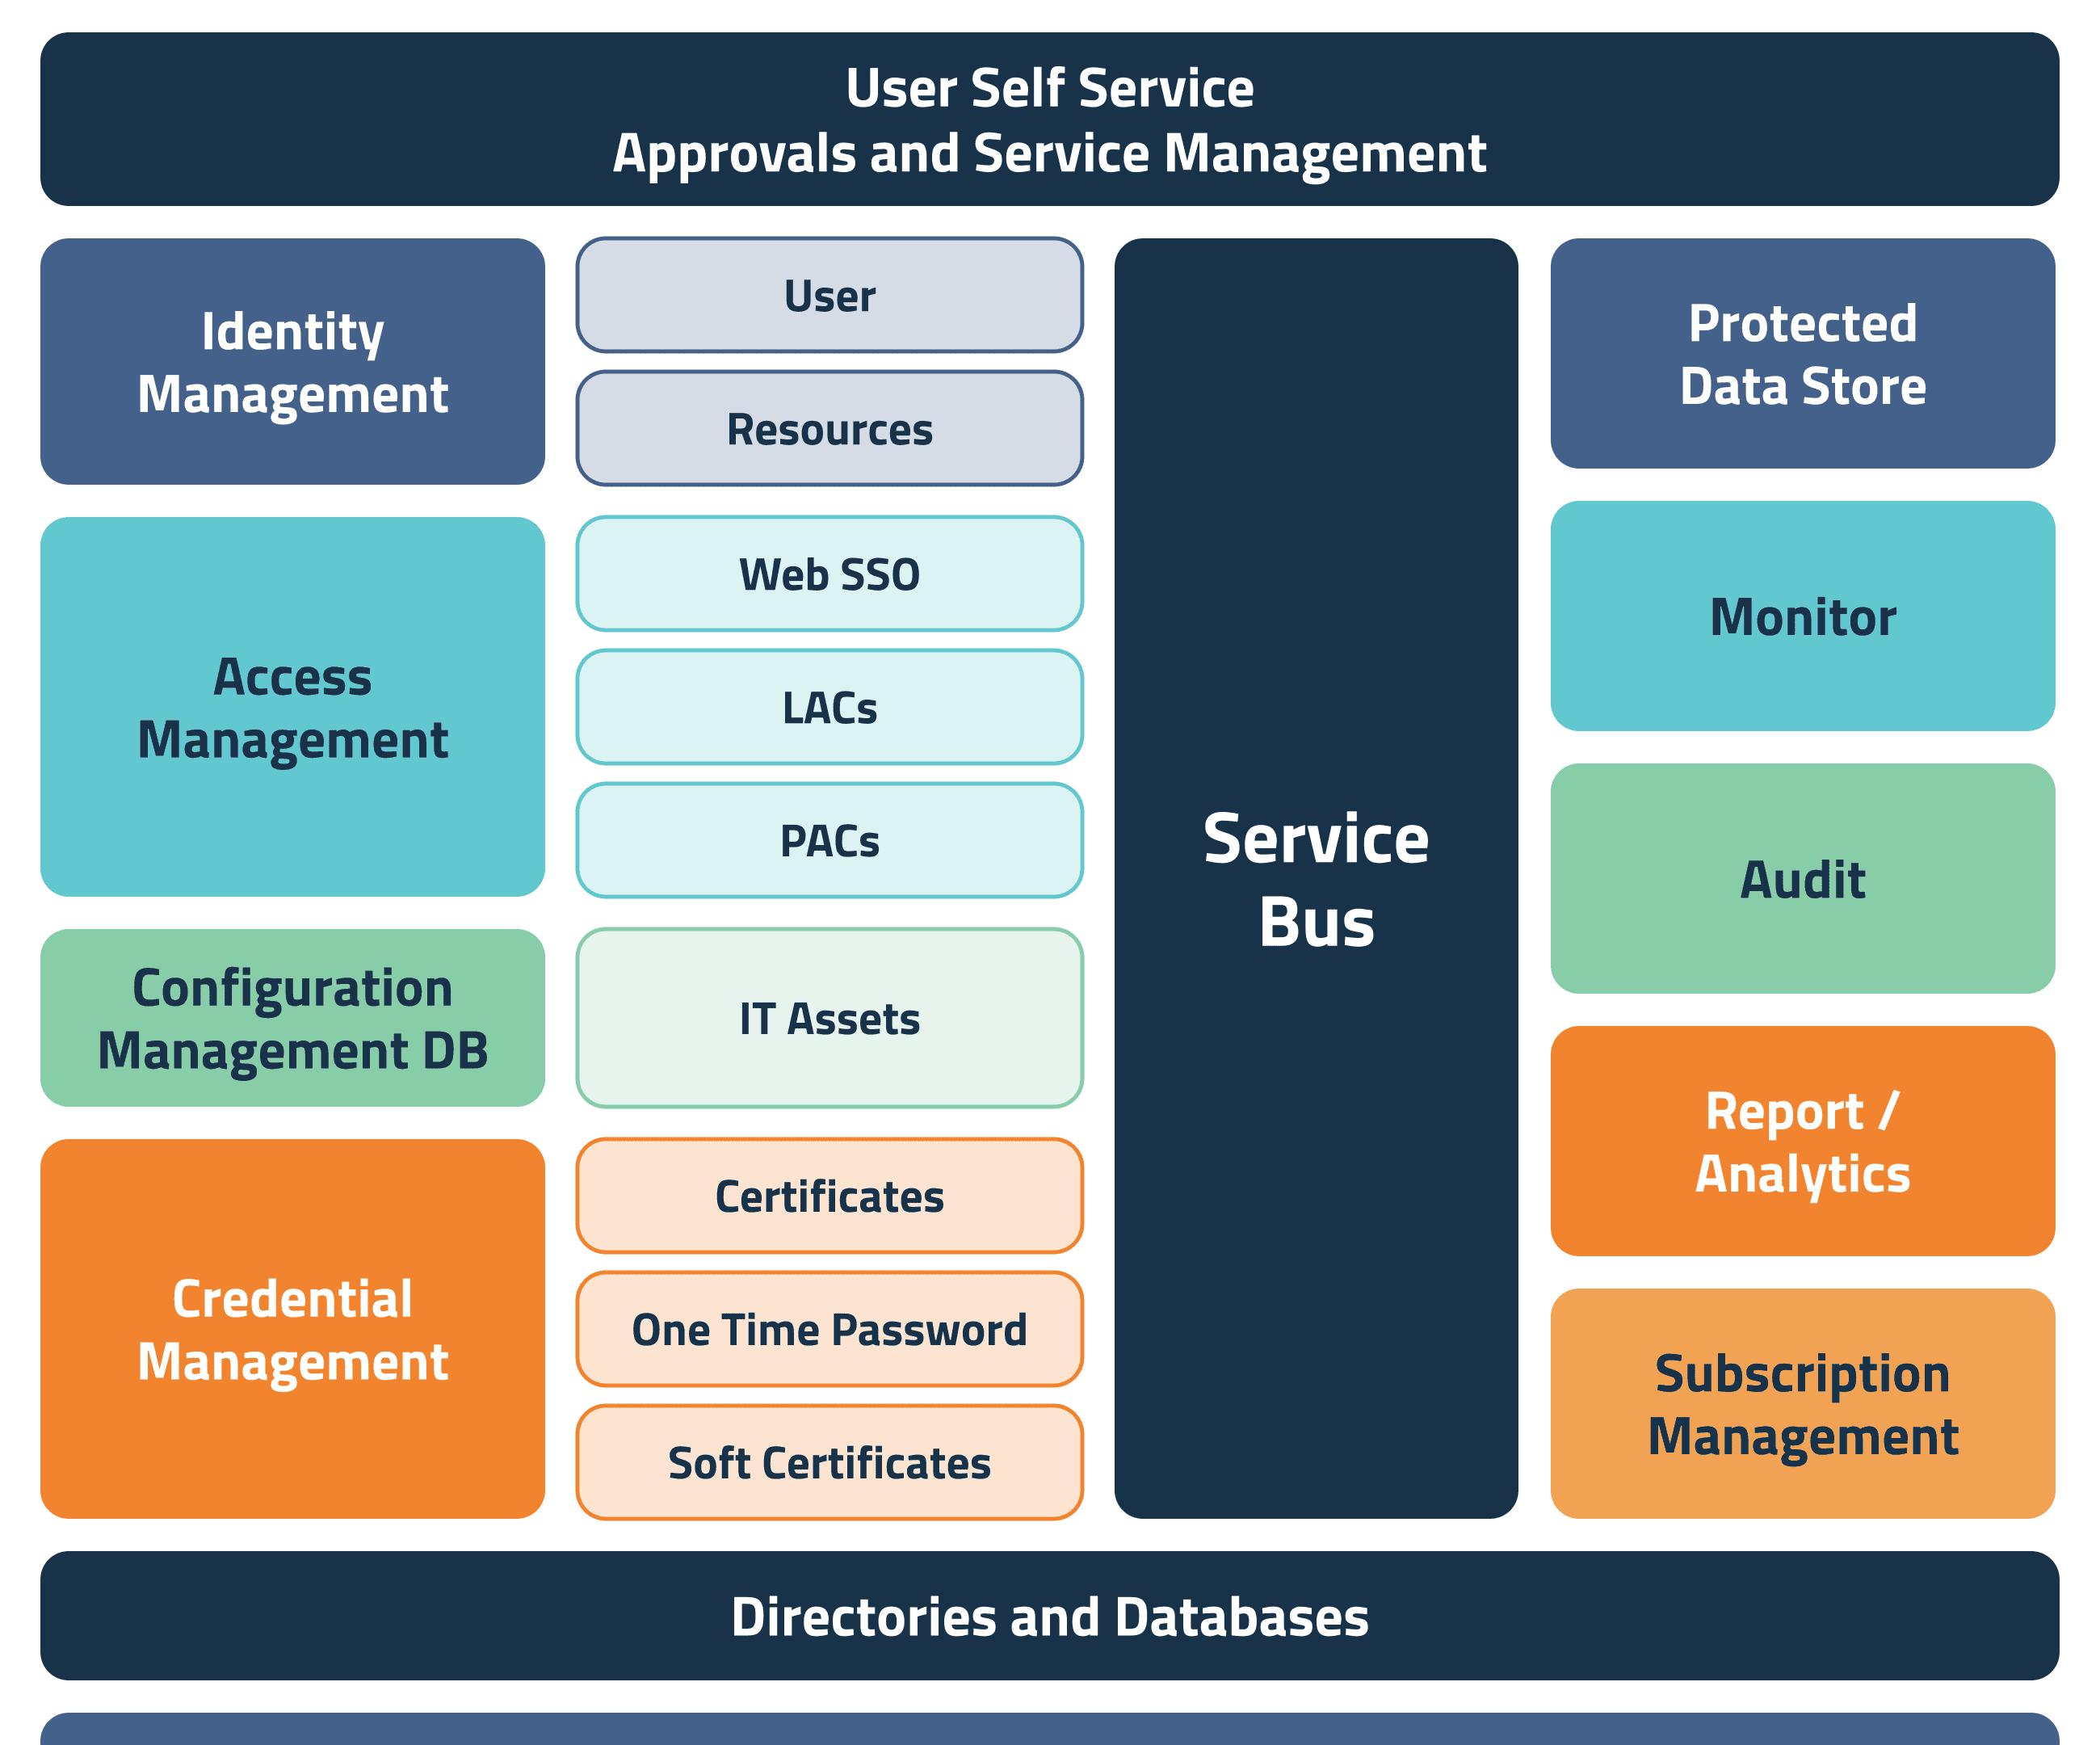
Figure 1: The Jellyfish Platform
Credentials
- Jellyfish Certificate Authority version 7.0 is Common Criteria certified to 29 April 2031 and NIAP listed.
- Cogito Group’s information security management system is certified to ISO/IEC 27001:2022.
- Services are assessed and available in multiple countries where they have their own certifications. Examples are:
- In Australia under the IRAP standard.
- In New Zealand under the Government Marketplace Security Assurance and Certification processes.
- Managed services run in Tier 3+ data centres with NV1/NV2 security-cleared staff.
- Hosted HSM and key management services run at FIPS 140-3 Level 2, and 3.
How it Works
- Establish trust anchors: Integrate CAs, HSMs, Directories, Devices, Services, PACS, LACS and cloud services.
- Automate lifecycles: Enrol, issue, rotate, renew and revoke credentials and certificates with policy.
- Enforce access: Apply identity and device-based controls across networks, applications and facilities.
- Observe and improve: Monitor compliance, receive alerts and feed telemetry to an existing SIEM.
Services at a Glance
The following services sit in four groups.
Certificates and PKI
Service | What it does |
|---|---|
Tracks every certificate from any CA, alerts before expiry and automates renewal from one dashboard | |
Hosted private CA, shared or dedicated, with hardware-protected keys, CRL and OCSP. Priced on active certificates, not issued ones | |
Common Criteria certified CA, hosted or on-premises | |
Issues and renews certificates with no manual steps over ACME, ACME+, SCEP, EST, CMP and AEX for Windows | |
Discovery and monitoring | Finds unknown certificates and keys on the network, in Windows stores, Java keystores and cloud accounts such as AWS, then alerts on them |
One web view across every Microsoft AD CS CA in a forest: expiries, failed requests, CRL and OCSP health | |
Hosts CRLs and runs OCSP so relying parties can confirm a certificate is still valid | |
Moves off AD CS, UniCERT, EJBCA, Entrust EASM, OpenSSL or Dogtag with old and new CAs running in parallel | |
Sovereign energy-sector PKI for CSIP-AUS, serving DNSPs, OEMs and aggregators |
Keys and Cryptography
Service | What it does |
|---|---|
Generates, stores, rotates and destroys keys in FIPS 140-2 Level 3 HSMs, with BYOK and HYOK for AWS, Azure, Google and Salesforce | |
Cloud HSM by subscription. Applications connect over standard PKCS #11 as if the HSM were local | |
Recovers encrypted data when a user leaves, forgets a password or loses a token | |
Encrypts Drive, Meet, Calendar and Docs content with keys Google cannot access | |
Finds every certificate, key and CA, rates quantum exposure and delivers PQC planning inputs, following the ASD LATICE framework | |
Hybrid and pure PQC key generation, signing and issuance (ML-KEM, ML-DSA), migrated one domain at a time |
Identity, Credentials and Signing
Service | What it does |
|---|---|
Identity governance, approvals, entitlements and audit, built on Midpoint | |
Issues and manages smartcards, PIV credentials, USB tokens and mobile credentials across their lifecycle | |
MFA, passkeys and SCIM provisioning | Phishing-resistant login, Azure AD single sign-on and automatic user provisioning from Entra ID |
Tamper-evident document signing, including on mobile with cloud HSM keys, and signing of executables and scripts | |
S/MIME encryption and signing in Outlook desktop and web, plus SEEMail gateway certificates |
Security Operations, People and Partners
Service | What it does |
|---|---|
Managed 24x7x365 monitoring, threat correlation and alert validation that extends or stands in for an in-house SOC | |
Design, build and sustainment of PKI and identity, Microsoft Root CA Program accreditation, tailored training | |
Connects applications and data into one coordinated security posture | |
Shared door access, meeting rooms, printers, lockers and visitor management for multi-tenant buildings | |
Resell, co-brand or white-label the platform as an MSP, reseller, integrator or technology partner |
Already Using One Service? Here is What Pairs With It
Each service below adds to the Jellyfish portal the customer already logs in to, so the second service needs no new platform.
Already using | Add next | Why it pairs |
|---|---|---|
CLM as a Service | PKI as a Service for private certificates. Automation agents (ACME, AEX, SCEP). Discovery agents | Public TLS certificates now last 200 days at most, then 100 days from March 2027 and 47 from March 2029. Manual renewal stops scaling |
PKI as a Service or Jellyfish CA | Hardware-protected CA keys. CogVA. Auto-enrolment for Windows, Intune, Linux and Kubernetes. Smartcard and email certificates | Moves the CA from software keys to HSM protection and puts it to work across devices, users and email |
Microsoft AD CS | AD CS Cartographer. CLM as a Service. Live CA migration | AD CS slows past 1 million certificates and stops responding at 2 million. Cartographer shows the estate first; migration then runs in parallel, with no cutover |
Key Management or HSM as a Service | PKI as a Service with an HSM-backed CA. BYOK and HYOK for AWS, Azure and Salesforce. Google Workspace CSE. Code signing. Key archival | Each one reuses keys the customer already holds in FIPS 140-2 Level 3 HSMs |
Cryptographic Stocktake | Ongoing discovery and monitoring. Post-quantum migration. CLM as a Service. Professional services for the transition plan | A stocktake is a baseline. Assets keep changing, and PSPF Requirement 0223 needs a transition plan built on the inventory |
IdAM or smartcard and credential management | MFA and passkeys. SCIM from Entra ID. PIV for physical and logical access. Smart Resources | One identity then drives every credential, door and login |
Security Operations Centre | Discovery and CMDB. Certificate monitoring and alerting. Endpoint security and vulnerability protection modules | Gives the SOC an inventory of certificates, keys and devices, and an alert before a certificate expires |
Utility PKI as a Service | Key Management as a Service. CLM as a Service for corporate certificates. Security Operations Centre | The platform that secures CER devices also covers the utility’s corporate IT |
Any government or defence service | Cryptographic Stocktake. Common Criteria certified Jellyfish CA. Professional services for accreditation | Stocktake deadlines fall from 31 December 2026, and Common Criteria certification meets high-assurance requirements |
MSP or reseller | Partner programme. White labelling. SecureSME MSP pricing | Sell PKI and CLM under your own brand to your own clients |
Why Now
The deadline for moving to post-quantum cryptography depends on which organisation is giving the advice. The Australian Signals Directorate (ASD) sets one of the most aggressive timelines: it recommends that organisations stop using traditional asymmetric cryptography, such as RSA and ECC, by the end of 2030. NIST, by comparison, deprecates these algorithms after 2030 and disallows them after 2035.
Five fixed dates make certificate automation and a cryptographic inventory urgent, whichever service a customer starts with.
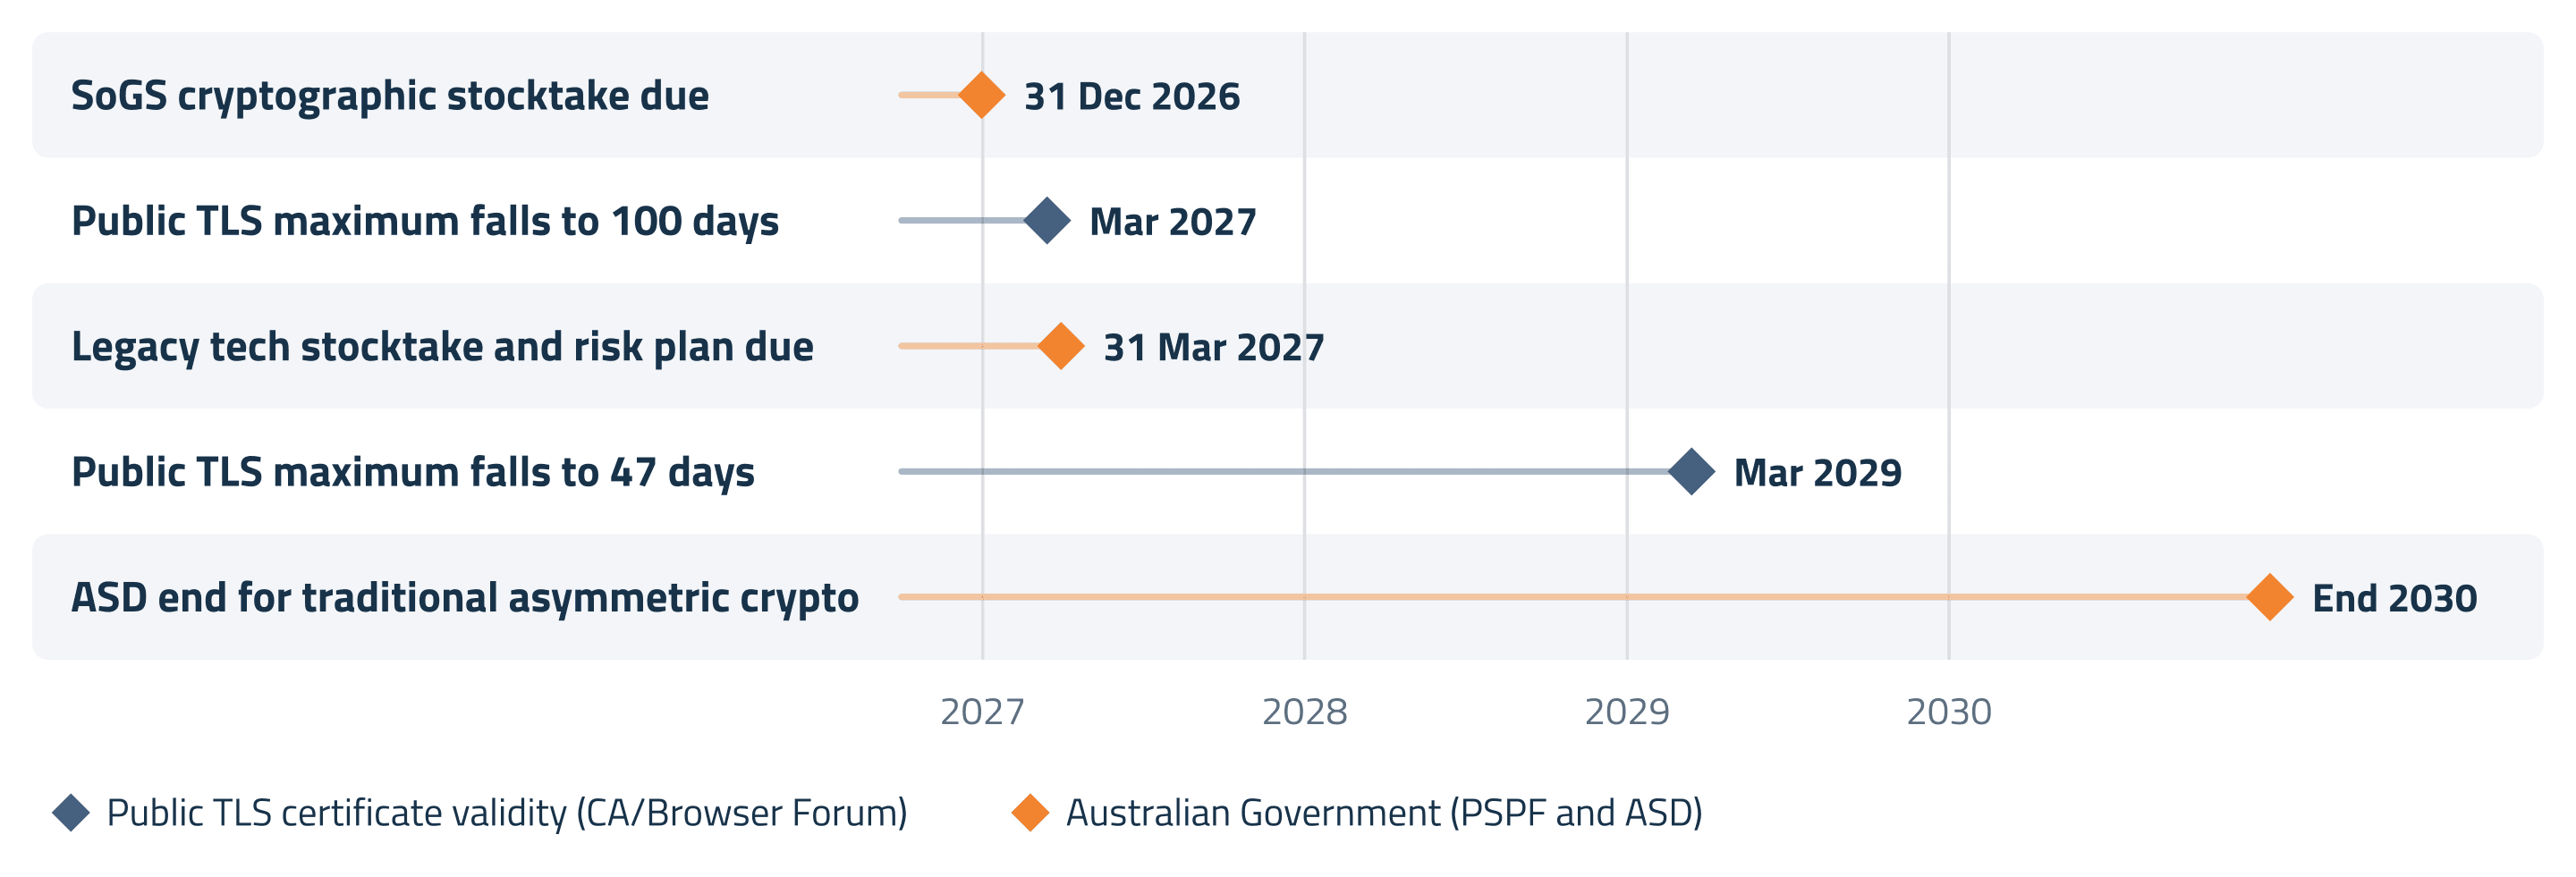
Figure 2: Certificate and Cryptography Deadlines to 2030
Public TLS certificates have been capped at 200 days since March 2026, and each later cut roughly halves the time between renewals (TLS and SSL Facts). Systems of Government Significance (SoGS) owe their stocktake first; other non-corporate Commonwealth entities plan under PSPF Requirement 0223 from 1 July 2026 (Cryptographic Stocktake).
Integrations
Jellyfish connects with commonly deployed enterprise systems to accelerate time-to-value:
- Certificate Authorities & PKI: Supports leading commercial and open-source CAs, including Microsoft AD CS, EJBCA, Entrust, UniCERT, DigiCert, Let’s Encrypt and Jellyfish Leviathan CA.
- HSM & Key Management: Works with major HSM vendors via Cryptoki/PKCS #11 and integrates with cloud key vaults and KMS platforms, such as AWS KMS and Azure Key Vault, for key custody and wrapping.
- Identity & Directories: Synchronises with Active Directory, Microsoft Entra ID, LDAP/SCIM sources and HR systems.
- Cloud & DevOps: Works with AWS Certificate Manager, Google Cloud Certificate Manager, Kubernetes cert-manager, F5 BIG-IP and Microsoft Intune.
- Service Management: Issues certificates through ServiceNow and BMC Remedy service requests.
- PACS & Facilities: Connects to leading physical access systems for unified credential control.
- Networks & CMDB: Network management and asset repositories to streamline approvals and record-keeping.
Deployment Options
Jellyfish is delivered as a service. All models deliver the same capability set, enabling consistent policy and operations.
- Cloud, as a service: Managed by Cogito Group for rapid rollout and minimal overhead.
- Hybrid: Operates alongside existing CAs, HSMs and directories while centralising lifecycle management.
- On-premises / Self-cloud: Fully isolated deployment for larger organisations with strict control and compliance requirements.
SecureSME Bundles and Starting Prices
SecureSME starts at US$399 a month for CLM and US$662 a month with your own CA, and the first month is free when you buy online with a card on file. Prices below come from the SecureSME price list in US dollars as at November 2026. They are a guide, not a quote.
Bundles
Bundle | Starting price | Includes | Best for |
|---|---|---|---|
US$399 per month | Tracking and renewal of every certificate from any CA. Add your own PKI later | Teams whose certificates come from other CAs | |
US$662 per month | CLM plus one online Root CA with a software key and two certificate templates | Teams issuing their own certificates for the first time | |
CLM and PKIaaS Custom Service | Priced to your business | Your own contract terms and SLAs, online or offline CAs with hardware-protected keys, a dedicated emergency phone line | Larger or regulated organisations |
Starting Estimates by Customer Type
Customer type | From (per month) |
|---|---|
Business with 50 to 250 staff | US$826.00 |
Managed service provider | US$883.55 |
Utilities or energy | US$1,965.00 |
Health | US$2,134.00 |
Government or defence supply | US$2,840.50 |
Finance with more than 250 staff | US$2,963.00 |
Common Add-ons
Add-on | Price (US$) |
|---|---|
Issuing CA online, hardware-protected key | 695.00 per CA per month |
Root CA offline, hardware-protected key | 1,299.00 per CA per month |
Automatic enrolment agent: ACME, ACME+, AEX, CMPv2, EST or SCEP | 132.00 per service per month |
Discovery agent: network, client, polling, hardware, cloud sync, scanner feed or PAM | 132.00 per service per month |
End entity certificates | 0.32 per certificate per month, discounted above 200 |
Professional services and helpdesk | 155.50 per hour |
AD CS Cartographer, on-premises | 4,500.00 per year per CA, per 5,000 certificates |
Jellyfish CA standalone, on-premises | 1,100.00 per year per CA |
Learn More
The Jellyfish Training Centre holds a factsheet or video for every service above. Good starting points:
- Jellyfish Product Datasheet: every module and integration on one page
- Functional comparison of PKI platforms and Jellyfish versus other certificate management platforms
- PKI as a Service: what the hosted service includes and how it is priced
- TLS and SSL Facts: the 200, 100 and 47 day certificate validity changes
- Prepare for PQC now: why the quantum transition starts with an inventory
- SecureSME demo: CLM and PKI as a Service for SMEs (video)
- Register a business and sign up for a SecureSME plan (video)
Get in Touch
Talk to us about adding a service, or book a demo.
- Phone: 1800 COGITO (1800 264 486) or +61 2 6140 4494, business hours
- Email: sales@cogitogroup.net
- Web: cogitogroup.net · securesme.com · training.cogitogroup.net